Why customers choose Tenable over Microsoft
Prioritize risk
Prioritize risk
Tenable Exposure View combines Tenable’s vulnerability priority rating (VPR) with an asset criticality rating (ACR) to objectively measure the risk of an asset, a business unit, or the whole organization.
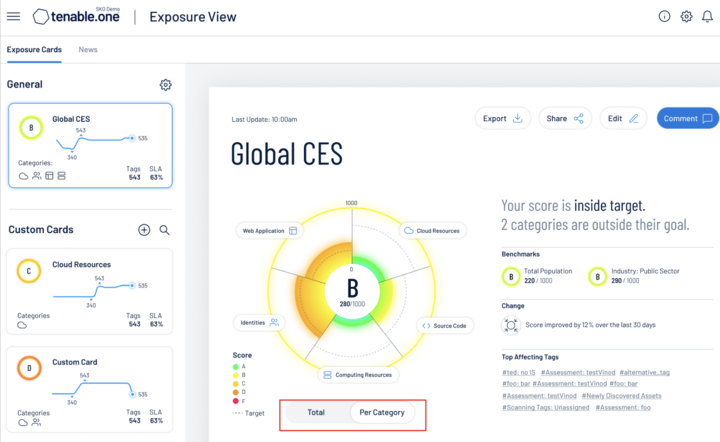
Security beyond the endpoint
Security beyond the endpoint
Tenable has complete visibility and assessment of your entire attack surface.
Reducing cyber risk and ensuring compliance requires understanding across traditional IT to the cloud to operational technology.
Tenable’s ability to log on to network devices and check for configuration and setting significantly reduces the rate of false-positives.
Coverage and accuracy
Coverage and accuracy
As of March 2026, Tenable Research has published more than 315K plugins covering over 116K CVEs. We continue to update and publish our vulnerability coverage and CVE count at tenable.com/plugins.
1 - Tenable blog link
153K K
Vulnerabilities assessed with 441,000+ plugins
814
Vulnerabilities disclosed by Tenable Research
< 24 hrs
Median time for coverage of high profile issues
Communicate risks
Communicate risk
Tenable enables communication by providing an extensive library of dashboards and reports to help facilitate communication with stakeholders such as senior leadership, IT and security colleagues, auditors, and the board.
Simplified licensing and cost
Simplified licensing and cost
Tenable pricing and licensing removes “security math,” double-charging and financial penalties for premium features common for Microsoft.
Compare Tenable to Microsoft

|

|
|
|---|---|---|
|
Tenable
Included: Industry’s broadest vulnerability coverage
|
Vulnerability and coverage accuracy
|
Microsoft
Not included: Not published
|
|
Tenable
Included: Exposure view combines Tenable’s vulnerability priority rating with an asset criticality score
|
Prioritization
|
Microsoft
Not included: Does not consider important business context
|
|
Tenable
Included: Wide variety of assets - endpoints, network devices, operational technology (OT), cloud workloads, web apps
|
Scope of coverage
|
Microsoft
Not included: Limited to the endpoints with an agent and basic SNMP-based capability
|
|
Tenable
Included: Extensive library of dashboards and reports
|
Dashboarding and reporting
|
Microsoft
Not included: Lack of dashboards and reports
|
|
Tenable
Included: Integration and support for the third-party remediation tools, remediation workflows
|
Vulnerability management tool ecosystem
|
Microsoft
Not included: Minimal integration with remediation tools like BigFix
|
|
Tenable
Included: Agent-based and agentless
|
Scanning technologies
|
Microsoft
Not included: Lacks Windows authenticated scanning
|
|
Tenable
Included: A truly vendor-agnostic Exposure view
|
Vendor agnostic
|
Microsoft
Not included: Best if you are 100% Microsoft
|
Recognized as a leader in exposure management by industry analysts

Tenable is a Leader in the 2025 Gartner® Magic Quadrant™ for Exposure Assessment Platforms

Tenable One
Request a demo
The world’s leading AI-powered exposure management platform.
Thank You
Thank you for your interest in Tenable One.
A representative will be in touch soon.
Form ID: 7469
Form Name: one-eval
Form Class: c-form form-panel__global-form c-form--mkto js-mkto-no-css js-form-hanging-label c-form--hide-comments
Form Wrapper ID: one-eval-form-wrapper
Confirmation Class: one-eval-confirmform-modal
Simulate Success